What Data Security for Airport Retail AI Systems Means for Travelers
Data security for airport retail AI means a traveler's personal information is kept safe, and that traveler stays in control. AI systems in airport shops use purchase history, location, and even biometric data to speed up services and improve safety. These tools check who you are in less than 2 seconds in 80% of cases. They also track movement through beacons or Wi-Fi to make offers just for you. Travelers deserve clear answers about how these systems work. Encryption, access controls, and anonymization keep that data safe. Travelers have rights too. They can consent to, access, or delete their information. Simple steps like adjusting privacy settings help them stay in charge.
Key Takeaways
Airport AI systems keep track of what you buy, where you go, and your face to give you faster service.
Encryption and access controls protect your personal data from hackers and misuse.
You can refuse facial scans and pick a manual ID check instead.
Change your phone settings, such as Bluetooth and Wi-Fi, to stop people from tracking your location without your permission.
Ask to delete your data after your trip to remove your info from airport systems.
What Airport Retail AI Knows About You
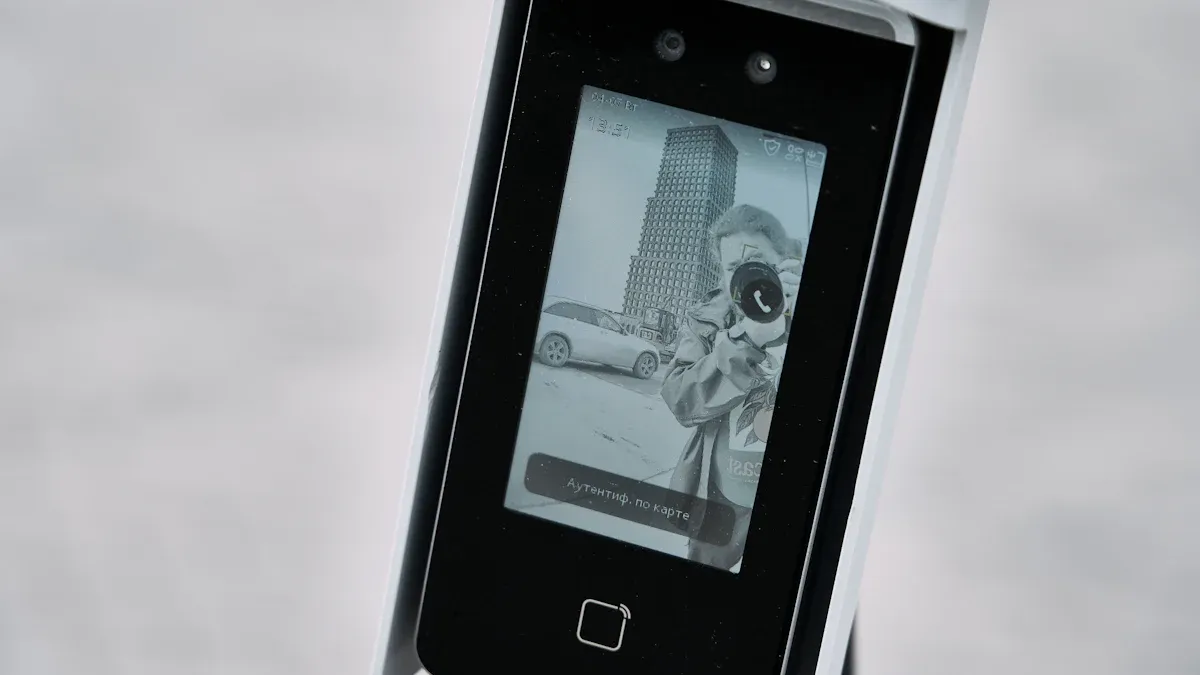
Airport shops collect different types of data to run their services. Travelers need to know what these systems track and why.
Purchase History and Loyalty Data
Retailers record every purchase a traveler makes in airport stores. This list shows what was bought, how much was spent, and when. Loyalty programs connect these purchases to a traveler’s account. The account may have a name, email, and flight details. AI systems look at this history to guess what a traveler might want next. A traveler who buys coffee each morning may see a cafe offer on the next trip. Algorithms use data to make these predictions. They compare one traveler’s habits to patterns from thousands of other shoppers. The result is a set of personalized services for each person. This approach saves time and makes shopping smoother. It also means a company has a detailed picture of a traveler’s spending habits.
Biometrics and Location Tracking
Many airports now use facial recognition and other biometrics at security and store kiosks. These tools can check a traveler’s identity in under 2 seconds in 80% of cases. A camera takes a picture of a face, and software matches it to a stored image. The process is fast and cuts down on paper documents. Location tracking works through beacons or Wi‑Fi signals. Beacons are small devices that notice a nearby phone. Wi‑Fi networks keep a record of which access points a device connects to. Both methods help retailers send offers based on where a traveler is. A person near a gate might get a discount for a close shop. This convenience raises privacy questions. A traveler may not know who sees that location data or how long a company keeps it. Clear rules and strong safeguards matter for every traveler.
Data Security: How Your Information Is Protected
Airport retail systems deal with private traveler details every day. Strong protections keep that data safe from misuse. Encryption, access controls, anonymization, and governance policies form the main defense.
Encryption and Access Controls
Encryption turns data into unreadable code. Only systems with the right digital key can unlock that code. A traveler’s payment details, loyalty account, and biometric template all stay encrypted at rest and in transit. This step blocks outsiders who try to grab data during transmission.
Access controls decide who can view or use that information. An airport retailer might let its point-of-sale terminal read a loyalty number. The same retailer would block a marketing server from seeing a full credit card number. Access logs record every request. These logs create a trail that shows which system touched which data and when. Auditors review these trails to catch misuse.
AI systems need instant access to governed data. Airports use automated policies instead of slow manual approvals. A rule engine checks each request against preset conditions. Does this system have the right role? Is the traveler’s consent on file? Does the request match an approved purpose? The engine grants or denies access in milliseconds. This speed keeps checkout lines moving without weakening data security.
Biometric verification speed does not compromise safety. A match in under 2 seconds in 80% of cases sounds risky to some travelers. The opposite is true. AI lowers false alarms and improves detection. A fast system compares a live face against a stored template using encrypted features. It never stores the raw image in an open database. The quick result comes from efficient matching, not from skipping safeguards. Encryption and access logs ensure only authorized systems see traveler data. An unauthorized device cannot decrypt the template or write to the log.
Anonymization and Data Governance
Anonymization removes personal identifiers from a dataset. A retailer might study shopping patterns without knowing who bought what. The company strips names, emails, and loyalty numbers. What remains is a record of items, times, and locations. Analysts use this anonymous data to improve store layouts and stock decisions. Travelers gain better service without exposing their identity.
Data governance sets the rules for the whole lifecycle. Who collects the data? How long does the company keep it? Who can share it with third parties? A governance framework answers these questions in writing. It assigns roles, defines retention periods, and requires regular audits. AI-driven systems follow these rules through automated checks. A governance engine can flag a request that violates a retention policy. It can block a transfer to an unapproved partner.
Threat detection adds another layer. Monitoring tools watch for unusual patterns. A sudden spike in access requests from one terminal might signal an attack. The system can lock that terminal and alert security staff. This proactive stance catches problems before they spread.
Governance also covers vendor contracts. Airports often work with multiple retailers and technology providers. Each contract must specify data security duties. Who encrypts the data? Who handles a breach notification? Clear terms prevent gaps that attackers exploit.
Travelers benefit from these protections even when they never see them. Encryption, access controls, anonymization, and governance work together. They let airports deliver fast, personalized service without sacrificing privacy. The next section explains the risks that remain and the rights travelers hold.
Data Security Risks and Your Rights
AI systems make shopping and security checks faster. But they also give bad actors new ways to attack. Travelers need to know the risks and the rights that keep them safe. Privacy laws in many places give travelers control over their personal information.
Data Breaches and Unauthorized Use
A data breach happens when someone without permission gets private information. In an airport retail system, a breach could leak purchase histories, loyalty accounts, or biometric templates. Attackers go after these systems because they hold valuable personal data. AI's speed does not remove this risk. It just changes how the risk looks.
Every connected device creates a new way in for attackers. A point-of-sale terminal, a beacon, or a Wi-Fi access point can be an entry point. Hackers look for weak spots in encryption or access controls. They may try to grab data while it travels. They may try to pretend to be an approved system. Each breach has serious results for travelers. Stolen biometric data cannot be replaced like a credit card. A traveler cannot get a new face.
Unauthorized use does not always come from outside attackers. An employee with access rights might look at data for personal reasons. A vendor might sell grouped data without permission. These inside risks need strong governance and regular audits. Access logs help spot unusual patterns. Automated alerts flag behavior that is not normal.
Privacy laws in many places give travelers specific protections. The General Data Protection Regulation (GDPR) in Europe and similar laws elsewhere set rules for handling data. These laws require companies to protect personal information. They impose fines for failures that lead to breaches. Travelers gain from these legal frameworks even when they cross borders. The law follows the data.
Consent, Access, and Deletion
Consent is a basic requirement for biometric collection. Airports and retailers must ask for permission before scanning a face or storing a biometric template. A traveler can say no. The system must offer other ways to verify identity or finish a purchase. This choice keeps control in the traveler's hands.
Access rights let travelers see what data a company holds. A traveler can ask to review their purchase history, location records, or biometric data. The company must respond within a legal timeframe. The traveler can check for errors or unauthorized entries. This openness builds trust between the traveler and the retailer.
Deletion rights give travelers the power to erase their data after a trip ends. A traveler can ask for removal of all personal information from airport retail systems. The company must comply unless legal duties require keeping it. A typical retention period lasts a few months for business purposes. After that window closes, the traveler can demand full deletion. Companies must confirm the deletion process is complete in writing.
These rights require action from the traveler. A company does not automatically delete data after a trip. The traveler must send a formal request. Most airports offer online portals or customer service contacts for this purpose. The process works best when travelers plan ahead. Knowing where to send a request makes the task simple.
Data security frameworks support these rights by enforcing limits on data use. Encryption keeps unauthorized parties from reading stored information. Access controls limit who can see sensitive records. Anonymization strips personal identifiers before analysis. Together, these protections create a safe space for AI-powered retail. Travelers can enjoy the convenience of personalized offers while keeping control over their information.
Practical Steps to Protect Your Data
Travelers have more power than they think. A few easy steps cut down on exposure and keep control in their hands.
Adjusting Privacy Settings
Travelers should begin with the settings on their own devices. Phone systems give you controls for location sharing, Bluetooth, and Wi-Fi. A traveler can shut off Bluetooth while walking through the terminal. This step stops nearby beacons from finding the device. Wi-Fi settings often let you forget a network after you use it. Turning off auto-join stops a phone from linking to airport networks on its own. These changes take under a minute and limit the data retailers can gather.
Loyalty program accounts also have privacy controls. Most retailers let members opt out of personalized marketing. A traveler can log in and review the consent choices. Many programs share purchase data with partners by default. Turning off that setting stops the flow of information to third parties. Travelers should check these options before every big trip. Retailers must honor opt-out requests under laws like the General Data Protection Regulation. A quick review of account settings keeps a traveler in charge of their own information.
Smart Sharing Habits
Every traveler makes choices about what to share at the point of sale. A loyalty card ties a purchase to a personal profile. Paying with cash or a general credit card leaves no such link. Travelers who value privacy can skip the loyalty scan for small purchases. They can still enjoy the ease of airport shops without building a detailed spending record. This habit limits the data available for profiling.
Biometric verification deserves the same care. Airports must ask for consent before scanning a face. A traveler can say no and ask for another check. Staff members can check a boarding pass or passport by hand. This choice may add a few seconds to the process. The trade-off gives the traveler control over a template that cannot be replaced. Travelers should also read privacy notices at kiosks. These notices explain what data the system collects and how long it stays. A few seconds of reading prevents surprises later. Smart sharing habits protect privacy without giving up the speed and personalized services that airports offer.
Airport retail AI systems build data security into every layer. Encryption, access controls, and governance policies protect traveler information. Biometric verification completes in under 2 seconds in 80% of cases. That speed comes with strong safeguards, not shortcuts. Travelers hold rights too. They can consent to biometric collection, access their records, and request deletion after a trip. Simple actions matter as well. Adjusting privacy settings and opting out of personalized marketing limit exposure. Smart sharing habits at checkout reduce the data trail. Travelers can enjoy the convenience of AI-powered retail. Staying informed and proactive keeps them in control of their journey.
FAQ
Can a traveler avoid facial recognition at airport retail kiosks?
Yes. The law requires permission before a store can scan your face. Travelers can say no. Staff must then check ID by hand, like looking at a boarding pass or passport.
How does a traveler request data deletion after a trip?
Travelers send an official request through the airport’s website or by calling customer service. The company must delete the data unless it has to keep it by law.
How do airport retail systems prevent data theft?
Systems use scrambling and rules about who can see data. Scrambling turns information into a secret code. Logs record every time data is read. Company rules set strict limits on how data can be used.
Does a 2-second verification time make it less safe?
No. Fast systems use quick comparisons, not weak protection. Scrambling keeps the face template safe. The speed comes from automated approval steps, not from skipping security.
Can travelers stop location tracking inside the terminal?
Yes. Turning off Bluetooth and Wi‑Fi keeps small devices and networks from finding your phone. Travelers can also turn off location services in phone settings for even more control.
See Also
Walmart Introduces New Self-Checkout Access Rules In 2025
Walgreens Self-Checkout Balances Convenience With Retail Hurdles
AI Powered Stores Are Shaping The Future Of Retail
Smart Electronics Vending Machines Transform Retail Shopping Experience
